
Our Journey through
the years



Cyber Security: from niche expertise to enterprise priority.
We bring together top international experts and researchers to discuss industry innovations, emerging risks, and the future of digital defense.
Dive into our archive to review the milestones of our evolutionary path. In a continuously evolving landscape, each edition represents a specific chapter of this growth, bringing together high-level technical sessions and strategic insights.


Across the Editions


Key Highlights & Speakers

Global Cybercrime Dynamics: A global perspective on hacker threats with Carlo Mauceli (CTO at Microsoft Italy) and Enrica Priolo.
Intelligence & Defense: The art of transforming information into active defense with Trellix.
The Golden Team: Integrating Business Continuity and Risk Management under the guidance of ANRA.
Cyber Resiliency & Cloud: The future of Cloud Native applications and European digital sovereignty with Entando, including deep dives into the AI Act.
Technical Deep Dives: Analyzing online banking fraud with Cleafy and attack techniques targeting Microsoft Active Directory infrastructures.
Key Highlights & Speakers
EU Strategy: Global Threat Management and the "Normative Firewall" with ENISA.
Supply Chain Security: The Impact of Open Source and Supply Chain Security with SAP Security Research.
AI & Security: Distinguished panel on the interaction between AI and Cyber Defense with experts from CEA, Cefriel e University of Cagliari.
Application Security: Deep dive on API Security (Checkmarx), Android Native Code, and testability patterns for Web Apps.
Emerging Tech: Focus on Smart Contract auditing and defense strategies against Advanced Persistent Threats(APTs).
Key Highlights & Speakers
Italian Cybercrime Trends (H1 2024) – Domenico Raguseo (Exprivia)
Deterministic GenAI & Reliable Outputs – Dinis Cruz (The Cyber Boardroom)
Ransomware Threat Intelligence & Analysis – Dario Fadda (Ransomfeed.it)
Secure Software Design & Reliability – Guido Mureddu (Pluribus One)
OWASP Top 10 for LLM & Mitigation – Federico Loi (IMQ Minded Security)
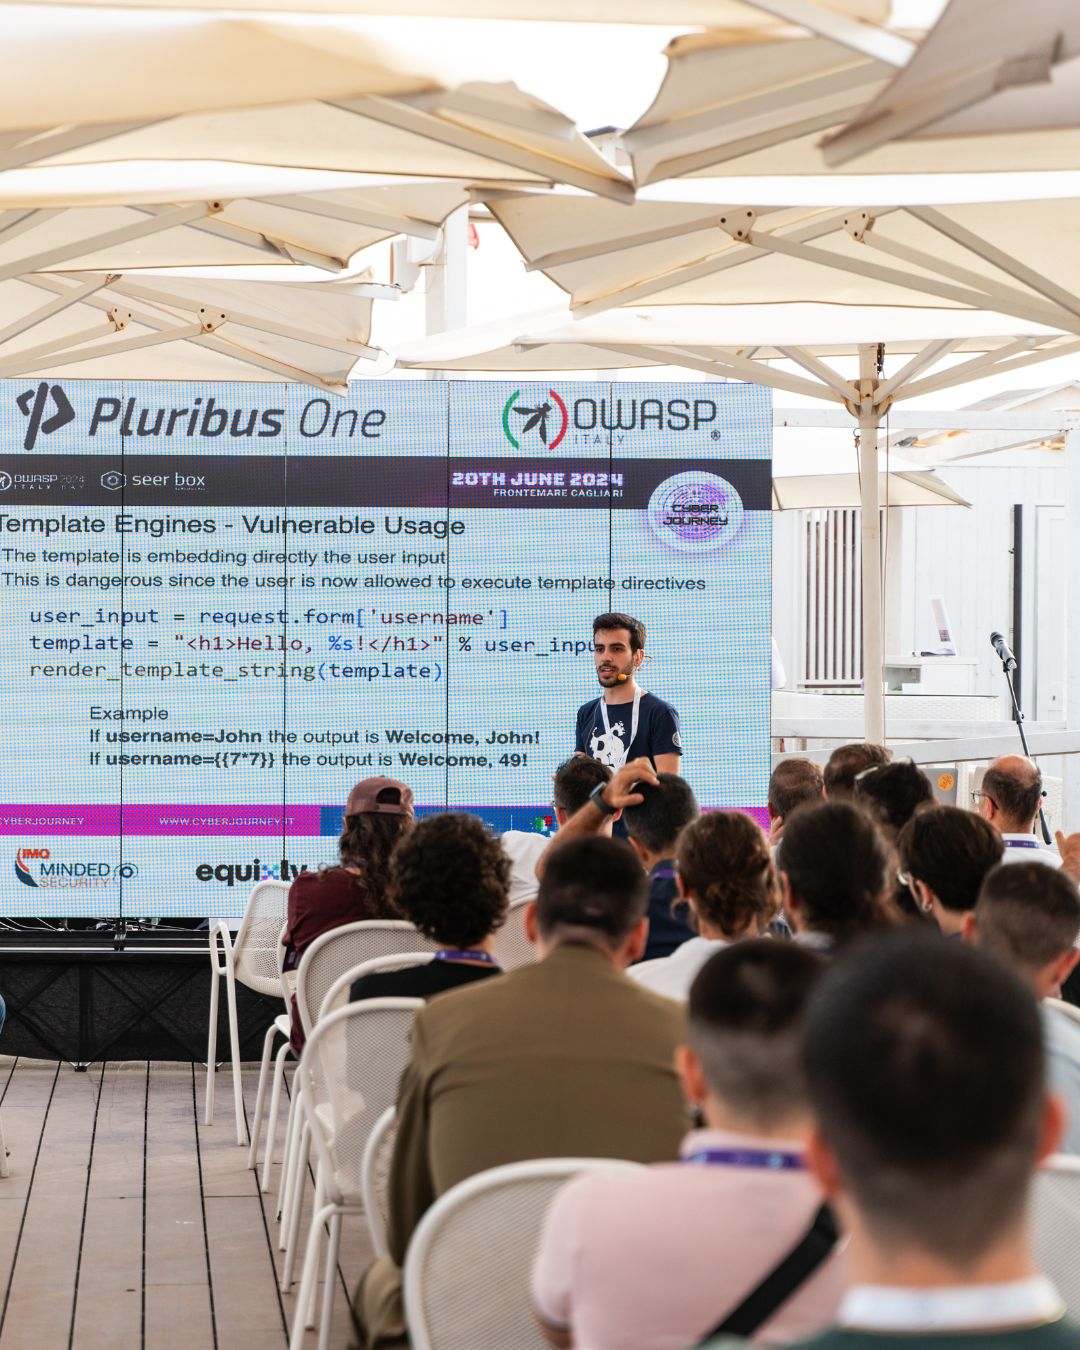
Server-Side Template Injection Vulnerabilities – Lorenzo Pisu (UniCa)
Key Highlights & Speakers
In Tools We Trust: The Reliability of Defense Systems – Martin Knobloch (Valtech)
Threat Modeling Pitfalls for Digital Credentials – Simone Onofri (W3C)
Security Criteria for AI and Blockchain Integration – Marco Morana (Avocado Systems)
LLM Security: From Helm Charts to Template Engines – Fabio Massacci (University Professor)
Human-Machine Interaction in the AI Era – Giacinto Fiore & Pasquale Viscanti (IA Spiegata Semplice)
Strategies for Evolving AppSec Programs – Luca Compagna (Endor Labs)
Building Product Security Teams: Practical Lessons – Francesco Paolo Giordano (PagoPA)
Future Directions for DevSecOps Models – Enrico Trasatti (Sogei)
Key Highlights & Speakers
The AI Security Moment: Why the Next Cybersecurity Crisis will be Algorithmic – Keynote: Vandana Verma (Snyk)
From Scratch: Creating An AppSec Program And Its Challenges – Julio Araujo (Rocket.Chat)
Spec-Driven Development: The Engineering Discipline That Secures, Economizes, and Certifies AI-Assisted Software – Jim Manico (Manicode Security)
Killing the Noise: AI Triage for High-Volume API Security Findings – Alessio Dalla Piazza (Equixly)
OWASP Mobile Application Security (MAS) - Project Updates – Sven Schleier (OWASP MAS)
It’s Giving Insecure Vibes: Secure Coding Literacy for Vibe Coders – Betta Lyon Delsordo (AWS)
From Code to Customer: Building a Zero-Trust Software Supply Chain at Enterprise Scale – Ritesh Ranjan & Ravinder Singh (Adobe)
LLM Prompt Injection: When Language Models Become an Attack Surface – Matteo Grollino (Relatech)